 新西兰前总理希普利:中国光伏储能为全球能源转型提供关键支撑 中新网 · 刚刚
 习近平APEC宣布:提供2000万推动亚太共同体合作 法广 RFI 中文 · 1 小时前
 建宏福苑火灾纪录库者因揭名医之女涉嫌「请枪」反被控四宗罪:吹哨者变被告 法广 RFI 中文 · 1 小时前
中文头条
暂时没有匹配的中文标题:以下是中文新闻机构的最新消息。

习近平APEC宣布:提供2000万推动亚太共同体合作
法广 RFI 中文 · 1 小时前
建宏福苑火灾纪录库者因揭名医之女涉嫌「请枪」反被控四宗罪:吹哨者变被告
法广 RFI 中文 · 1 小时前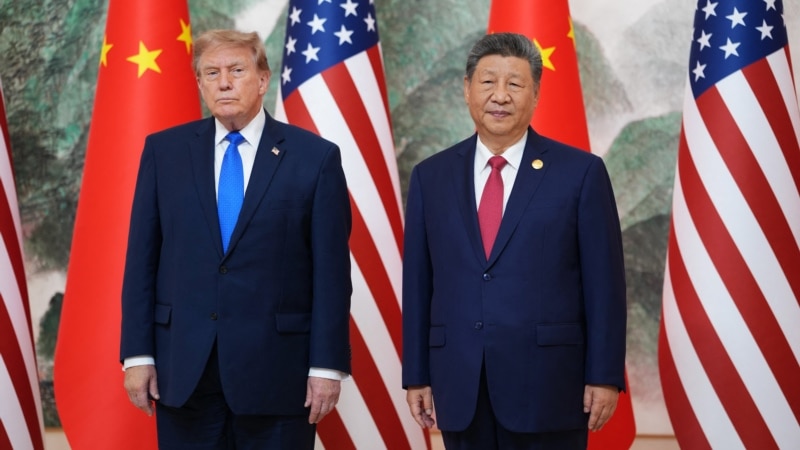
特朗普总统在深圳对习近平说,希望美中共同推动结束俄乌战争
美国之音 中文 · 1 小时前
APEC的特色服飾:從克林頓皮衣到深圳「鯤鵬展翅」絲巾
BBC 中文 · 2 小时前
Anthropic上市:七位即將成為億萬富翁的創辦人
BBC 中文 · 2 小时前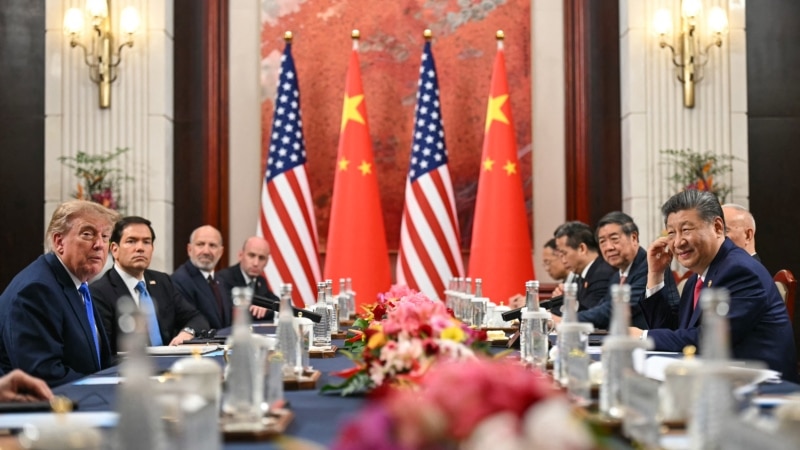
特朗普总统在深圳先会普京,与习近平的双边峰会聚焦经贸分歧
美国之音 中文 · 3 小时前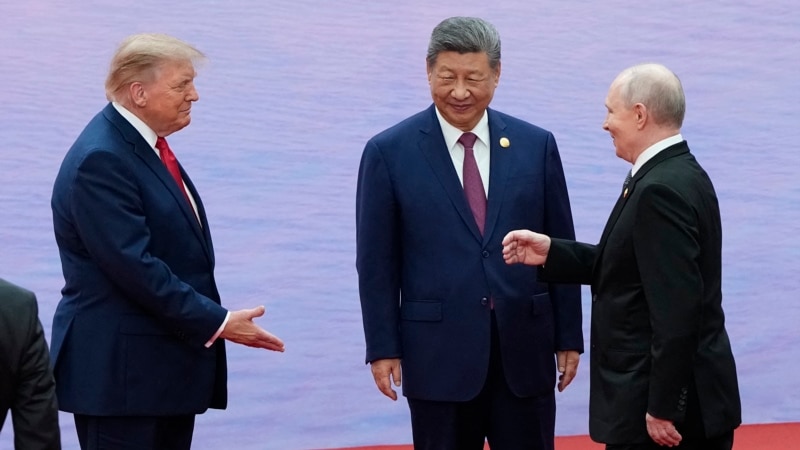
美中俄深圳会晤前夕,美国国会议员对北京能否促普京结束战争看法不一
美国之音 中文 · 8 小时前
中美俄「三巨頭」坐在了一起,世界正滑向大國共管嗎?
BBC 中文 · 9 小时前- 第六届世界华文教育大会在海南召开 中新网 · 刚刚
- 新西兰前总理希普利:中国光伏储能为全球能源转型提供关键支撑 中新网 · 刚刚
- 月面聚光烧砖、远程送电、开采水冰:中国新技术推动人类从“探月”迈向“驻月” 中新网 · 1 小时前
- 梵谷名畫62.7億落槌創紀錄 納粹時期藏家爭議落幕 中央社 国际 · 2 小时前
- 克宮:普丁與川普會談42分鐘 會後「心情極佳」 中央社 国际 · 2 小时前
- 美官員稱科技當機潮非惡意網攻 專家指系統老舊釀禍 中央社 国际 · 2 小时前
- 中美俄元首会晤不会成为另一个雅尔塔会议 纽约时报中文网 · 5 小时前
- 习近平与高市早苗简短会面,中日关系无解冻迹象 纽约时报中文网 · 6 小时前
- 特朗普抵达深圳:展示友好关系,无视间谍丑闻 纽约时报中文网 · 7 小时前
- 为填补乌克兰预算缺口,欧盟提议由各成员国向乌克兰提供一笔额外的450亿欧元贷款 法广 RFI 中文 · 10 小时前
Exploited right now
Flaws CISA has confirmed attackers are using, added in the last 14 days. Patch these first.
- CVE-2024-10441: Synology DiskStation Manager (DSM)Synology DiskStation Manager (DSM) Improper Encoding or Escaping of Output Vulnerability · EPSS 1.3% · 70th percentile · CISA · 添加于 2026-11-18
- CVE-2026-40217: BerriAI LiteLLMBerriAI LiteLLM Unprotected Alternate Channel Vulnerability · EPSS 17% · 97th percentile · CISA · 添加于 2026-11-18
- CVE-2026-90817: Vanderbilt University Research Electronic Data Capture (REDCap)Vanderbilt University Research Electronic Data Capture (REDCap) Code Injection Vulnerability · EPSS 3.7% · 90th percentile · CISA · 添加于 2026-11-18
- CVE-2026-90436: Apache AxisApache Axis Unsafe Reflection Vulnerability · EPSS 1.1% · 67th percentile · CISA · 添加于 2026-11-18
- CVE-2026-115731: Perforce Puppet EnterprisePerforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability · EPSS 0.7% · 53rd percentile · CISA · 添加于 2026-11-17
- CVE-2026-114713: UnrealIRCd UnrealIRCdUnrealIRCd Improper Neutralization of Delimiters Vulnerability · EPSS 0.5% · 41st percentile · CISA · 添加于 2026-11-13
- CVE-2026-123039: Check Point Multiple ProductsCheck Point Multiple Products Incorrect Permission Assignment for Critical Resource Vulnerability · EPSS 1.9% · 80th percentile · CISA · 添加于 2026-11-13
- CVE-2026-124194: Microsoft OfficeMicrosoft Office Outlook Missing User Interaction for Potentially Unsafe Action Vulnerability · EPSS 1.6% · 76th percentile · CISA · 添加于 2026-11-10
Government cyber advisories
From CISA, the UK NCSC, CERT-EU and Canada's Cyber Centre.
- SmarterTools security advisory (AV26-1177)Canadian Centre for Cyber Security ·
- JetBrains security advisory (AV26-1176)Canadian Centre for Cyber Security ·
- Cisco security advisory (AV26-1175)Canadian Centre for Cyber Security ·
- F5 security advisory (AV26-1174)Canadian Centre for Cyber Security ·
- GNU security advisory (AV26-1173)Canadian Centre for Cyber Security ·
- GitHub security advisory (AV26-1172)Canadian Centre for Cyber Security ·
- Google security advisory (AV26-1171)Canadian Centre for Cyber Security ·
- Oracle Corporation security advisory (AV26-1170)Canadian Centre for Cyber Security ·
New critical vulnerabilities
27 rated critical (CVSS 9.0+) in the last 3 days by the U.S. National Vulnerability Database.
- CVE-2026-114881 · CVSS 9.1 · EPSS 0.5% · 44th percentileVulnerability in the Document Management and Collaboration product of Oracle E-Business Suite (component: Attachments). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attack ·
- CVE-2026-91469 · CVSS 9.4 · EPSS 0.4% · 38th percentileVulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected are 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 and 15.1.1.0.0. Easily exploitable vulnerability allows unauthe ·
- CVE-2026-115139 · CVSS 9.3 · EPSS 0.4% · 33rd percentileVulnerability in the Oracle Hyperion Infrastructure Technology product of Oracle Hyperion (component: Installation and Configuration). The supported version that is affected is 11.2.26.0.000. Easily exploitable vulnerability allows unauth ·
- CVE-2026-114956 · CVSS 9.3 · EPSS 0.4% · 33rd percentileVulnerability in the Oracle Hyperion Planning product of Oracle Hyperion (component: Security). The supported version that is affected is 11.2.26.0.000. Easily exploitable vulnerability allows unauthenticated attacker with network access ·
- CVE-2026-114934 · CVSS 9.3 · EPSS 0.4% · 29th percentileVulnerability in the PeopleSoft Enterprise PeopleTools product of Oracle PeopleSoft (component: Integration Broker). Supported versions that are affected are 8.61-8.63. Easily exploitable vulnerability allows unauthenticated attacker with ·
- CVE-2026-101691 · CVSS 9.3 · EPSS 0.4% · 29th percentileVulnerability in the Oracle Mobile Field Service product of Oracle E-Business Suite (component: Admin UI). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attacker with netwo ·
- CVE-2026-91507 · CVSS 9.3 · EPSS 0.3% · 27th percentileVulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.1.0. Easily exploitable vulnerability allows unauthenticated ·
- CVE-2026-130778 · CVSS 10Incus before 7.6.0 contains an authentication bypass vulnerability that allows remote attackers to authenticate as any trusted certificate by appending its public certificate to their presented TLS client chain. Attackers can append the ser ·
Ransomware claims, last 7 days
150 claims posted by ransomware groups in 7 days, 25 in the last 24 hours. These are the criminals' own claims, not verified; Spike counts them and names no victim. Data: ransomware.live.
By country
 美国61
 加拿大8
 德国7
 印度5
 阿拉伯联合酋长国
 墨西哥3
 日本3
 澳大利亚3
 英国3
 越南2
By sector
Most active groups
thegentlemen 18qilin 15N0n 14PixelLeaks 13Vortex 7Curious Worm 6rhysida 6Booba Project 6lockbit5 5akira 5
Cyber 家新闻机构, every 5 minutes
7 of 8 security 家新闻机构 answered in the last check.
- US enlists private firms to cut scammers off from victims’ cashHelp Net Security ·
- Africa Retakes Top Spot as Most Attacked Region, Led by Nigeria SurgeDark Reading ·
- PHP Readies Critical Security Updates to Patch Another RCE FlawSecurityWeek ·
- Game consoles and Teslas are slipping past OT network segmentationHelp Net Security ·
- AI agents inherit employee access, and nobody’s watching how they use itHelp Net Security ·
- PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19The Hacker News ·
- Palo Alto Networks to Buy AI Startup Applied Compute for $4.5 BillionSecurityWeek ·
- Quantum position verification could lock remote hackers out, NIST showsHelp Net Security ·
- Ransomware access brokers are moving their deals off public forumsHelp Net Security ·
- Azure Linux 4 puts the OS behind Microsoft’s cloud services on your VMs at no extra license feeHelp Net Security ·
- Russia's Cold Relic APT Turns One Cloud Breach Into AnotherDark Reading ·
- Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilitiesCyberScoop ·
Companies disclosing cyber incidents
U.S. public companies must file Form 8-K Item 1.05 with the SEC within four business days of deciding a cyber incident is material. Filings from the last 120 days, from SEC EDGAR.
- Park Dental Partners, Inc. (PARK)Form 8-K, Item 1.05 · filed 2026-10-13 · all filings
- Astrana Health, Inc. (ASTH)Form 8-K, Item 1.05 · filed 2026-09-23 · all filings
- BOSTON SCIENTIFIC CORP (BSX)Form 8-K, Item 1.05 · filed 2026-09-08 · all filings
- Park Dental Partners, Inc. (PARK)Form 8-K, Item 1.05 · filed 2026-09-01 · all filings
- Nutex Health Inc. (NUTX)Form 8-K, Item 1.05 · filed 2026-08-31 · all filings
- AMGEN INC (AMGN)Form 8-K, Item 1.05 · filed 2026-07-31 · all filings
- River Financial Corp (RVRF)Form 8-K, Item 1.05 · filed 2026-07-30 · all filings
Internet outages by country, last 24 hours
Disruptions detected by IODA at Georgia Tech from routing, active probing and traffic data. A disruption can be a cut cable, a power failure, an attack or a government shutdown; IODA reports the drop, not its cause.
 伯利兹 Criticalrouting (BGP), Google traffic · · country risk
 危地马拉 CriticalGoogle traffic · · country risk
 哥伦比亚 CriticalGoogle traffic · · country risk
 哥斯达黎加 CriticalGoogle traffic · · country risk
 厄瓜多尔 CriticalGoogle traffic · · country risk
 尼加拉瓜 CriticalGoogle traffic · · country risk
 洪都拉斯 CriticalGoogle traffic · · country risk
 土库曼斯坦 Criticalactive probing, routing (BGP) · · country risk
 刚果(金) Criticalrouting (BGP), Google traffic · · country risk
 海地 CriticalGoogle traffic, routing (BGP) · · country risk
Threat actors in the news, 7 days
Groups named in security newsroom headlines and government advisories. Linked to their MITRE ATT&CK profile where one exists.
Malware seen in the last 24 hours
888 indicators of compromise shared on abuse.ch ThreatFox.
Unknown malware 145Mirai 138IClickFix 62Vidar 47Raven Stealer 45ClearFake 29XWorm 25Unknown Loader 24Formbook 21Sliver 20php.shin_webshell 18Agent Tesla 18
Spike Pro can watch the vendors and products your organization runs (for example Fortinet, Citrix, Microsoft Exchange) and notify your team the moment CISA confirms exploitation, a critical vulnerability is published, or a government advisory names them. Spike Pro →
全世界在搜索的:网络安全观察
警报 冲突、扰乱或丑闻 · 快速升温 快速升温 · 增长中 growing · 脉搏 0–100: 90+ 爆发 · 70+ 火爆 · 40+ 正在升温


