Les titres en français
Aucun titre francophone ne correspond pour l'instant : voici les dernières nouvelles des rédactions francophones.

Rencontre entre Trump, Poutine, et Xi: la réunion inédite entre les trois dirigeants débute en Chine
franceinfo · à l'instant
Trump-Poutine-Xi: début de la rencontre trilatérale historique
France 24 · à l'instant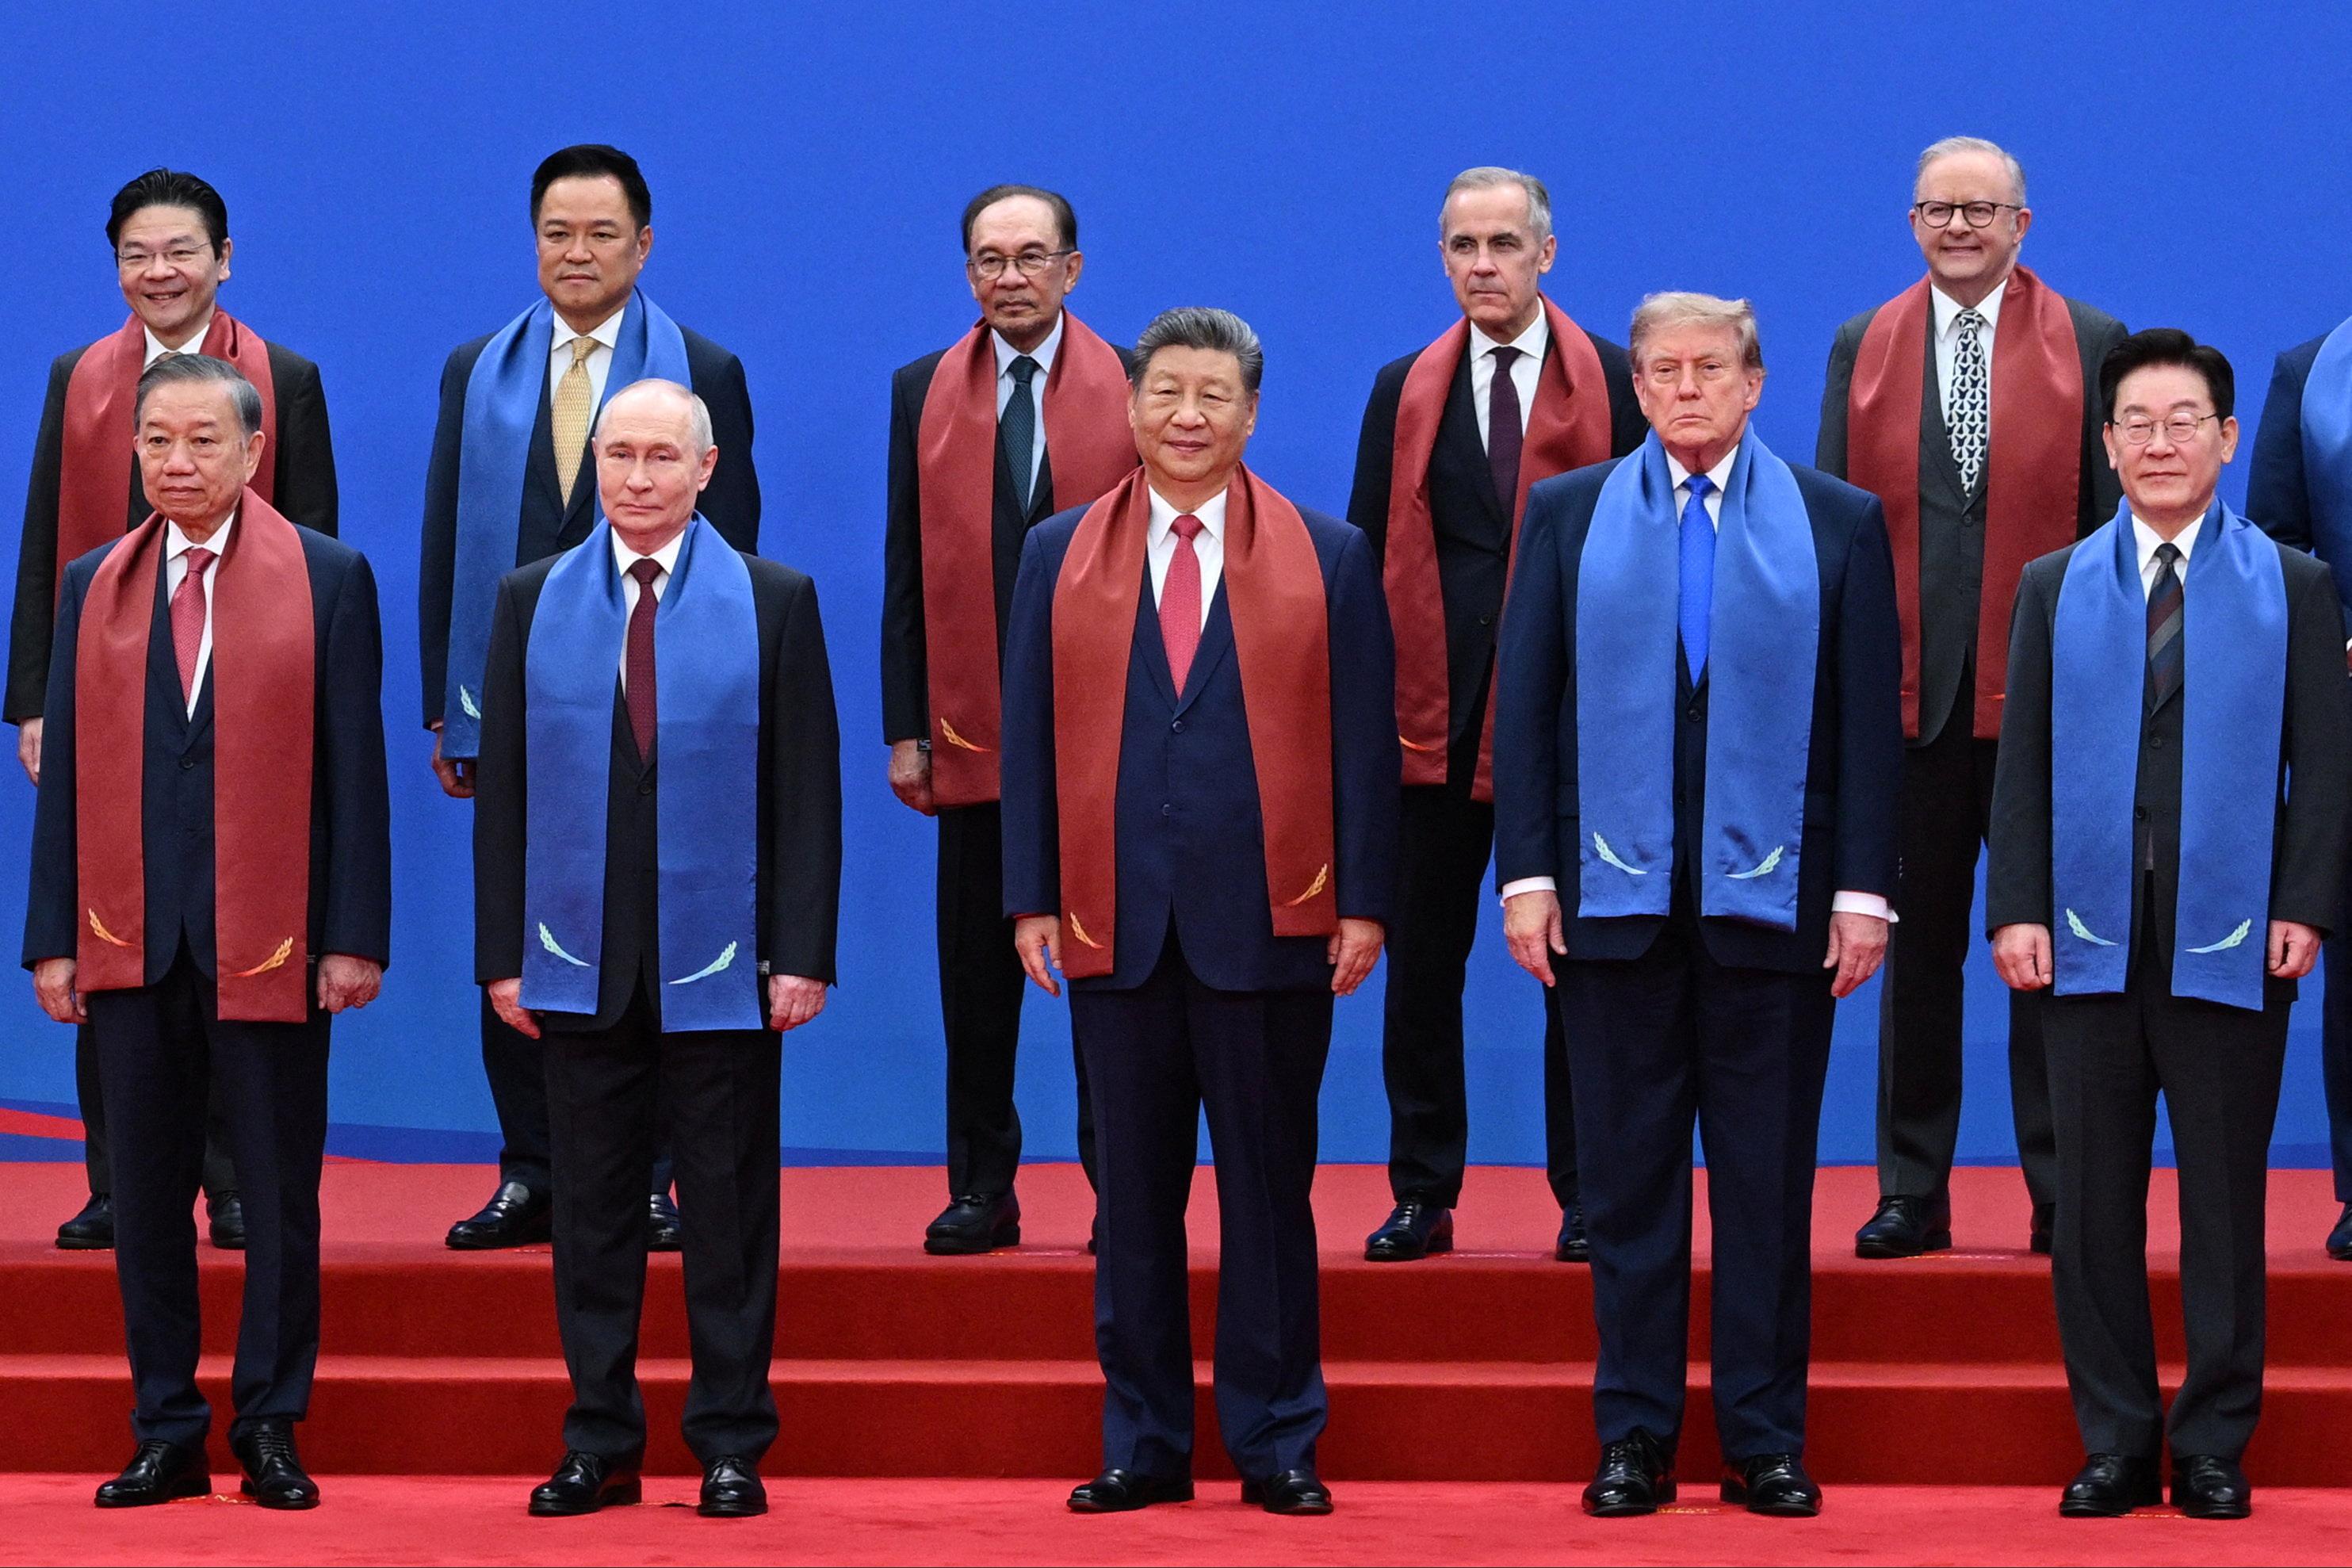
EN DIRECT - À Shenzhen, Xi Jinping, Donald Trump et Vladimir Poutine réunis pour un sommet trilatéral inédit
Le Figaro · à l'instant
La crue historique du Rhône à Sierre et Chippis, un «échec collectif» du gouvernement valaisan et de son administration
Le Temps · à l'instant
La grippe débarque, déjà deux régions en pré-épidémie
20 Minutes · à l'instant
"La colère des élus est très forte": face à la baisse de dotation prévue, des maires placent un ruban noir sur les panneaux de leur ville
franceinfo · à l'instant
L'économiste Gabriel Zucman veut alerter sur "les milliardaires" qui "menacent nos démocraties" dans un nouveau manifeste
franceinfo · il y a 1 h
À la Une: GTA VI, le plus grand divertissement de tous les temps…
RFI · il y a 1 h- 🔴 Shenzhen en direct: la réunion tripartite entre Trump, Poutine et Xi a débuté France 24 · à l'instant
- Tableau de Van Gogh adjugé 173 M€ à New York pour clore un litige lié à l’ère nazie Euronews · à l'instant
- Tours télécoms: le rachat du géant IHS par MTN franchit un cap décisif en zone Cemac Jeune Afrique · à l'instant
- Emirates en tête du classement TIME 2027 des compagnies aériennes, sans Européenne dans le top 10 Euronews · à l'instant
- 🔴 Sommet de Shenzhen en direct: Poutine est arrivé, la réunion tripartite avec Trump et Xi va commencer France 24 · il y a 1 h
- Bertrand Méheut, l’ancien patron de Canal+, est mort à 75 ans 20 Minutes · il y a 1 h
- EN DIRECT - Présidentielle 2027: en choisissant Mélenchon, Tondelier «tourne le dos» à la «tradition pro-européenne des écologistes», estime Glucksmann Le Figaro · il y a 1 h
- Au Cameroun, l’administration s’invite dans la bataille électorale Jeune Afrique · il y a 1 h
- «Un dirigeant d’exception»: Bertrand Meheut, l’ancien patron de Canal+, est mort Le Figaro · il y a 1 h
- "C'est mon ami", lance Trump en retrouvant Poutine à Shenzhen Euronews · il y a 1 h
Exploited right now
Flaws CISA has confirmed attackers are using, added in the last 14 days. Patch these first.
- CVE-2024-10441: Synology DiskStation Manager (DSM)Synology DiskStation Manager (DSM) Improper Encoding or Escaping of Output Vulnerability · EPSS 1.3% · 70th percentile · CISA · ajouté le 2026-11-18
- CVE-2026-40217: BerriAI LiteLLMBerriAI LiteLLM Unprotected Alternate Channel Vulnerability · EPSS 17% · 97th percentile · CISA · ajouté le 2026-11-18
- CVE-2026-90817: Vanderbilt University Research Electronic Data Capture (REDCap)Vanderbilt University Research Electronic Data Capture (REDCap) Code Injection Vulnerability · EPSS 3.7% · 90th percentile · CISA · ajouté le 2026-11-18
- CVE-2026-90436: Apache AxisApache Axis Unsafe Reflection Vulnerability · EPSS 1.1% · 67th percentile · CISA · ajouté le 2026-11-18
- CVE-2026-115731: Perforce Puppet EnterprisePerforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability · EPSS 0.7% · 53rd percentile · CISA · ajouté le 2026-11-17
- CVE-2026-114713: UnrealIRCd UnrealIRCdUnrealIRCd Improper Neutralization of Delimiters Vulnerability · EPSS 0.5% · 41st percentile · CISA · ajouté le 2026-11-13
- CVE-2026-123039: Check Point Multiple ProductsCheck Point Multiple Products Incorrect Permission Assignment for Critical Resource Vulnerability · EPSS 1.9% · 80th percentile · CISA · ajouté le 2026-11-13
- CVE-2026-124194: Microsoft OfficeMicrosoft Office Outlook Missing User Interaction for Potentially Unsafe Action Vulnerability · EPSS 1.6% · 76th percentile · CISA · ajouté le 2026-11-10
Government cyber advisories
From CISA, the UK NCSC, CERT-EU and Canada's Cyber Centre.
- SmarterTools security advisory (AV26-1177)Canadian Centre for Cyber Security ·
- JetBrains security advisory (AV26-1176)Canadian Centre for Cyber Security ·
- Cisco security advisory (AV26-1175)Canadian Centre for Cyber Security ·
- F5 security advisory (AV26-1174)Canadian Centre for Cyber Security ·
- GNU security advisory (AV26-1173)Canadian Centre for Cyber Security ·
- GitHub security advisory (AV26-1172)Canadian Centre for Cyber Security ·
- Google security advisory (AV26-1171)Canadian Centre for Cyber Security ·
- Oracle Corporation security advisory (AV26-1170)Canadian Centre for Cyber Security ·
New critical vulnerabilities
27 rated critical (CVSS 9.0+) in the last 3 days by the U.S. National Vulnerability Database.
- CVE-2026-114881 · CVSS 9.1 · EPSS 0.5% · 44th percentileVulnerability in the Document Management and Collaboration product of Oracle E-Business Suite (component: Attachments). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attack ·
- CVE-2026-91469 · CVSS 9.4 · EPSS 0.4% · 38th percentileVulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected are 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 and 15.1.1.0.0. Easily exploitable vulnerability allows unauthe ·
- CVE-2026-115139 · CVSS 9.3 · EPSS 0.4% · 33rd percentileVulnerability in the Oracle Hyperion Infrastructure Technology product of Oracle Hyperion (component: Installation and Configuration). The supported version that is affected is 11.2.26.0.000. Easily exploitable vulnerability allows unauth ·
- CVE-2026-114956 · CVSS 9.3 · EPSS 0.4% · 33rd percentileVulnerability in the Oracle Hyperion Planning product of Oracle Hyperion (component: Security). The supported version that is affected is 11.2.26.0.000. Easily exploitable vulnerability allows unauthenticated attacker with network access ·
- CVE-2026-114934 · CVSS 9.3 · EPSS 0.4% · 29th percentileVulnerability in the PeopleSoft Enterprise PeopleTools product of Oracle PeopleSoft (component: Integration Broker). Supported versions that are affected are 8.61-8.63. Easily exploitable vulnerability allows unauthenticated attacker with ·
- CVE-2026-101691 · CVSS 9.3 · EPSS 0.4% · 29th percentileVulnerability in the Oracle Mobile Field Service product of Oracle E-Business Suite (component: Admin UI). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attacker with netwo ·
- CVE-2026-91507 · CVSS 9.3 · EPSS 0.3% · 27th percentileVulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.1.0. Easily exploitable vulnerability allows unauthenticated ·
- CVE-2026-130778 · CVSS 10Incus before 7.6.0 contains an authentication bypass vulnerability that allows remote attackers to authenticate as any trusted certificate by appending its public certificate to their presented TLS client chain. Attackers can append the ser ·
Ransomware claims, last 7 days
150 claims posted by ransomware groups in 7 days, 25 in the last 24 hours. These are the criminals' own claims, not verified; Spike counts them and names no victim. Data: ransomware.live.
By country
 États-Unis
 Canada
 Allemagne
 Inde5
 Émirats arabes unis
 Mexique
 Japon
 Australie
 Royaume-Uni
 Viêt Nam
By sector
Most active groups
thegentlemen 18qilin 15N0n 14PixelLeaks 13Vortex 7Curious Worm 6rhysida 6Booba Project 6lockbit5 5akira 5
Cyber rédactions, every 5 minutes
7 of 8 security rédactions answered in the last check.
- US enlists private firms to cut scammers off from victims’ cashHelp Net Security ·
- Africa Retakes Top Spot as Most Attacked Region, Led by Nigeria SurgeDark Reading ·
- PHP Readies Critical Security Updates to Patch Another RCE FlawSecurityWeek ·
- Game consoles and Teslas are slipping past OT network segmentationHelp Net Security ·
- AI agents inherit employee access, and nobody’s watching how they use itHelp Net Security ·
- PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19The Hacker News ·
- Palo Alto Networks to Buy AI Startup Applied Compute for $4.5 BillionSecurityWeek ·
- Quantum position verification could lock remote hackers out, NIST showsHelp Net Security ·
- Ransomware access brokers are moving their deals off public forumsHelp Net Security ·
- Azure Linux 4 puts the OS behind Microsoft’s cloud services on your VMs at no extra license feeHelp Net Security ·
- Russia's Cold Relic APT Turns One Cloud Breach Into AnotherDark Reading ·
- Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilitiesCyberScoop ·
Companies disclosing cyber incidents
U.S. public companies must file Form 8-K Item 1.05 with the SEC within four business days of deciding a cyber incident is material. Filings from the last 120 days, from SEC EDGAR.
- Park Dental Partners, Inc. (PARK)Form 8-K, Item 1.05 · filed 2026-10-13 · all filings
- Astrana Health, Inc. (ASTH)Form 8-K, Item 1.05 · filed 2026-09-23 · all filings
- BOSTON SCIENTIFIC CORP (BSX)Form 8-K, Item 1.05 · filed 2026-09-08 · all filings
- Park Dental Partners, Inc. (PARK)Form 8-K, Item 1.05 · filed 2026-09-01 · all filings
- Nutex Health Inc. (NUTX)Form 8-K, Item 1.05 · filed 2026-08-31 · all filings
- AMGEN INC (AMGN)Form 8-K, Item 1.05 · filed 2026-07-31 · all filings
- River Financial Corp (RVRF)Form 8-K, Item 1.05 · filed 2026-07-30 · all filings
Internet outages by country, last 24 hours
Disruptions detected by IODA at Georgia Tech from routing, active probing and traffic data. A disruption can be a cut cable, a power failure, an attack or a government shutdown; IODA reports the drop, not its cause.
 Belize Criticalrouting (BGP), Google traffic · · country risk
 Guatemala CriticalGoogle traffic · · country risk
 Colombie CriticalGoogle traffic · · country risk
 Costa Rica CriticalGoogle traffic · · country risk
 Équateur CriticalGoogle traffic · · country risk
 Nicaragua CriticalGoogle traffic · · country risk
 Honduras CriticalGoogle traffic · · country risk
 Turkménistan Criticalactive probing, routing (BGP) · · country risk
 RD Congo Criticalrouting (BGP), Google traffic · · country risk
 Haïti CriticalGoogle traffic, routing (BGP) · · country risk
Threat actors in the news, 7 days
Groups named in security newsroom headlines and government advisories. Linked to their MITRE ATT&CK profile where one exists.
Malware seen in the last 24 hours
888 indicators of compromise shared on abuse.ch ThreatFox.
Unknown malware 145Mirai 138IClickFix 62Vidar 47Raven Stealer 45ClearFake 29XWorm 25Unknown Loader 24Formbook 21Sliver 20php.shin_webshell 18Agent Tesla 18
Spike Pro can watch the vendors and products your organization runs (for example Fortinet, Citrix, Microsoft Exchange) and notify your team the moment CISA confirms exploitation, a critical vulnerability is published, or a government advisory names them. Spike Pro →
Ce que le monde recherche — Cyberveille
Alerte conflit, perturbation ou scandale · Monte vite monte vite · En progression growing · Pouls 0–100: 90+ Explosif · 70+ Brûlant · 40+ Ça chauffe


 · il y a 26 h

