 Trump dice que EE.UU. y China buscan el fin de la guerra en Ucrania y coinciden sobre Irán Clarín · hace 1 h
Titulares en español
Ningún titular en español coincide por ahora: estas son las últimas noticias de las redacciones en español.
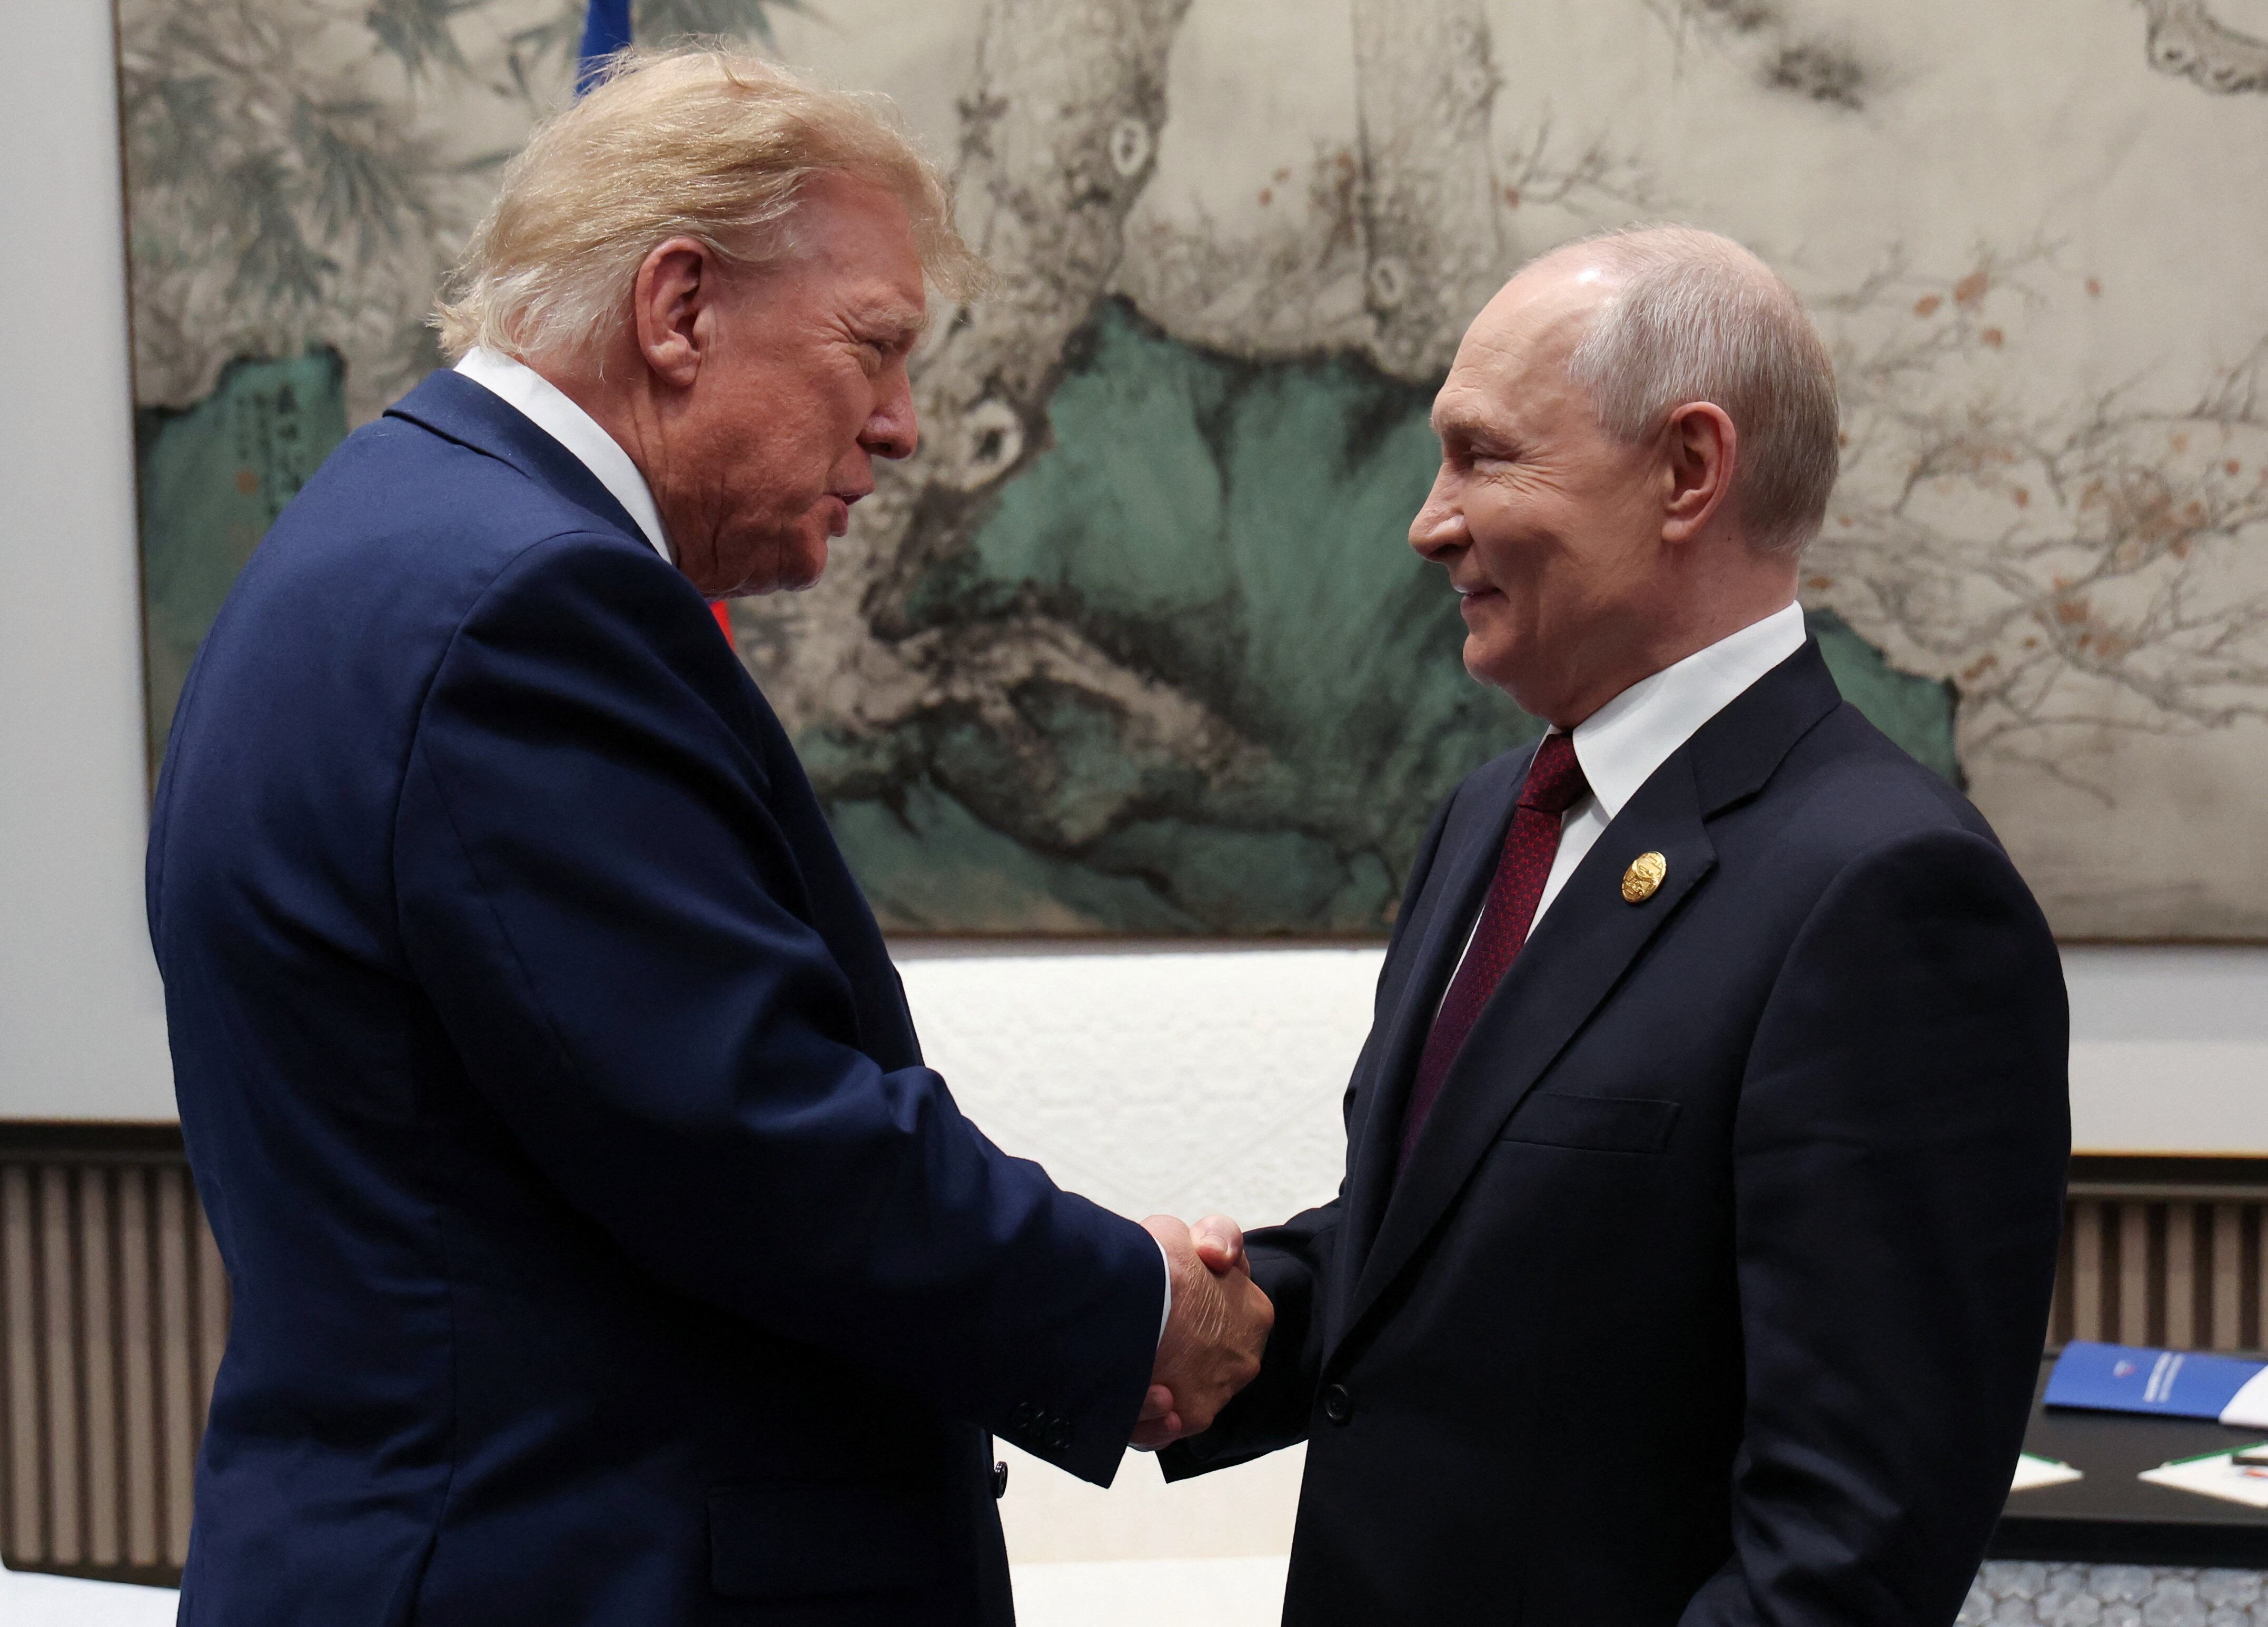
Xi recibe a Trump y Putin en el inicio de una reunión trilateral histórica
El País · ahora mismo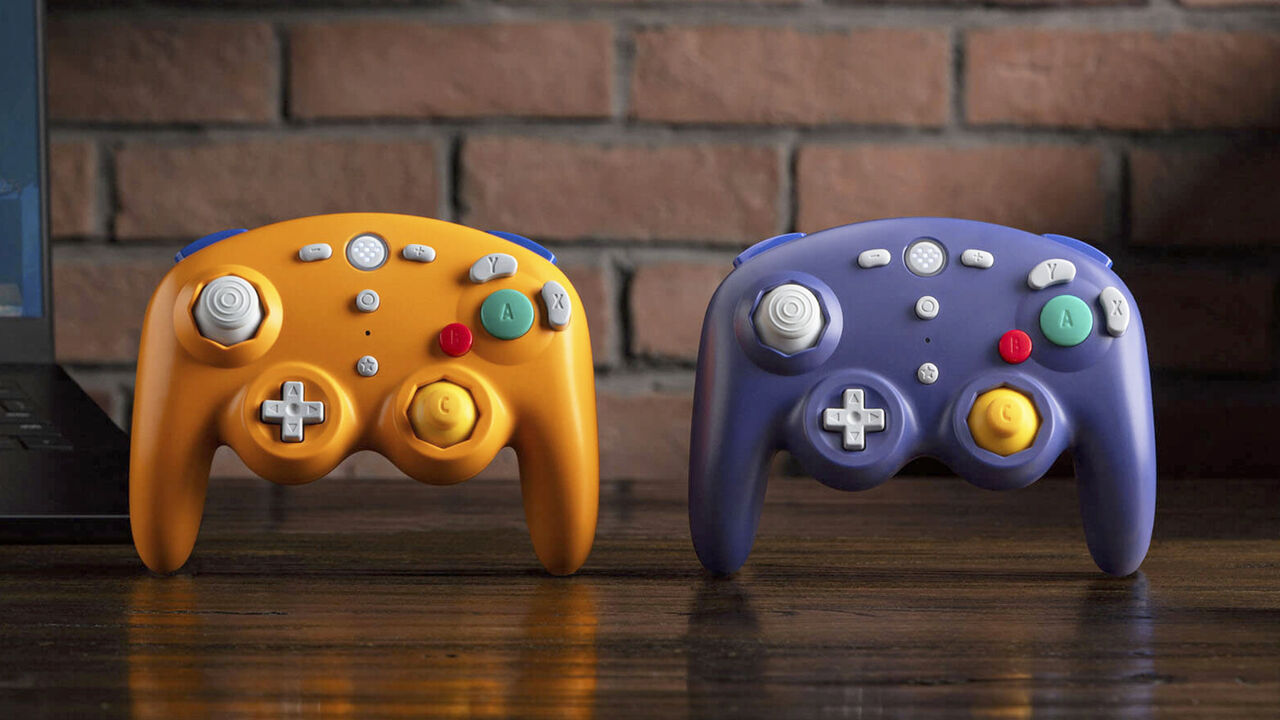
El mando de GameCube vuelve en morado y naranja, ahora sin cables y con sticks magn�ticos
Vandal · hace 1 h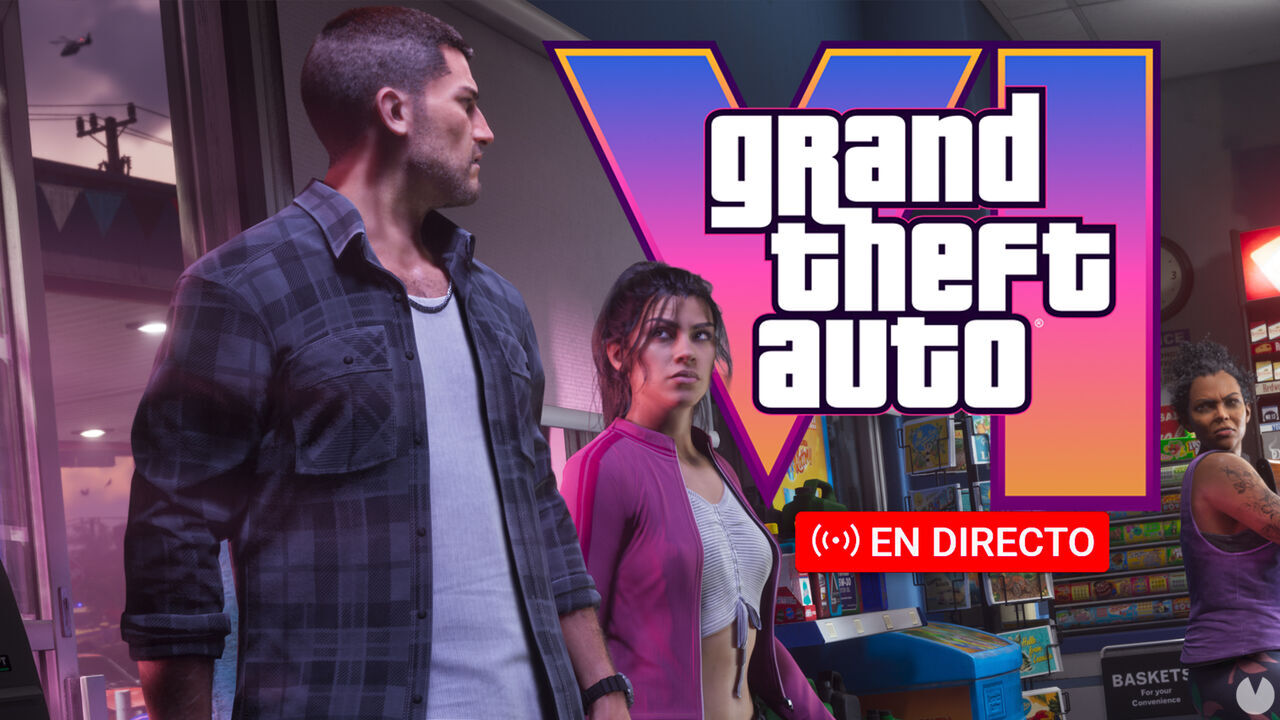
GTA 6, en directo: An�lisis, �ltimas hora y reacciones durante su lanzamiento en PS5 y Xbox Series
Vandal · hace 1 h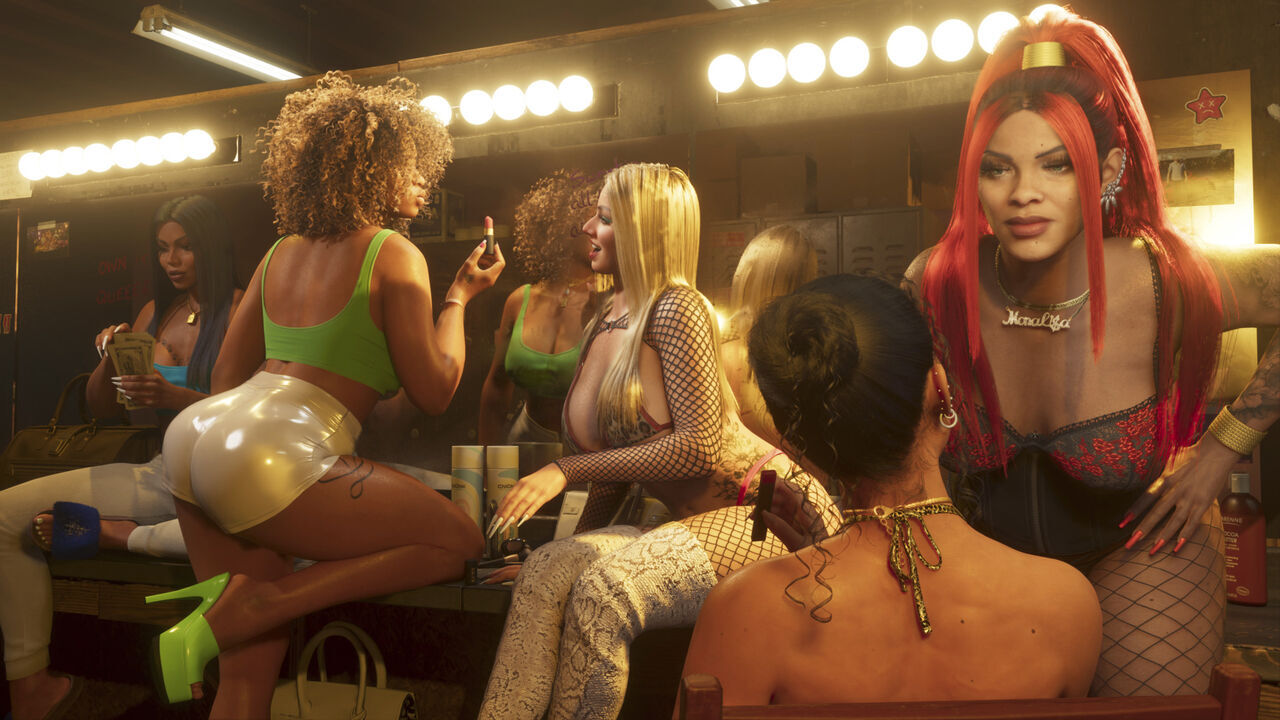
Rockstar explica por qu� GTA 6 ya no permite contratar prostitutas, una opci�n presente desde GTA 3
Vandal · hace 1 h
Un hombre se entrega a la Policía tras matar a su mujer de 47 años en Parla: "He degollado a mi pareja, aquí están las llaves"
El Mundo · hace 1 h
La crisis en Medio Oriente supone la "mayor amenaza" para la seguridad energética de la historia, advierte la AIE
France 24 Español · hace 1 h
Trump dice que EE.UU. y China buscan el fin de la guerra en Ucrania y coinciden sobre Irán
Clarín · hace 1 h
Ángela perdió a su hijo de 17 años en una mina: "Todavía no se había casado, no había disfrutado lo hermoso que la vida tenía preparado para él"
Clarín · hace 1 h- En directo: Putin ha llegado; la reunión trilateral con Trump y Xi está por comenzar France 24 Español · ahora mismo
- Trump y Putin vuelven a negociar cara a cara en China el futuro de Ucrania: "El presidente ruso es mi amigo" El Mundo · hace 1 h
- ¡Ojo, conductor! Pico y placa en Bucaramanga para el jueves 19 de noviembre de 2026: estas son las placas que no pueden circular El Tiempo · hace 1 h
- ¡Evite multas! Pico y placa en Cali para el jueves 19 de noviembre de 2026: consulte qué carros no pueden circular El Tiempo · hace 1 h
- ¡Ojo, conductor! Pico y placa en Pereira para el jueves 19 de noviembre de 2026: estos carros y motos no pueden circular durante 14 horas El Tiempo · hace 1 h
- "Pensaron que estaba muerto": chocó con una camioneta, lo golpeó un profesor de jiu jitsu y terminó en terapia intensiva Clarín · hace 2 h
- 🔴 En directo: Trump y Xi dialogan en China antes de una inédita cumbre trilateral con Putin France 24 Español · hace 2 h
- Vicente Luis Mora, primer español en lograr el National Book Award, el premio literario más importante de EEUU El Mundo · hace 2 h
- Casi 50.000 evacuados en al estado de Odisha por la llegada del potente ciclón Akvan en India programada para el viernes DW Español · hace 3 h
- La crisis en Medio Oriente amenaza la seguridad energética mundial, advierte la AIE DW Español · hace 3 h
Exploited right now
Flaws CISA has confirmed attackers are using, added in the last 14 days. Patch these first.
- CVE-2024-10441: Synology DiskStation Manager (DSM)Synology DiskStation Manager (DSM) Improper Encoding or Escaping of Output Vulnerability · EPSS 1.3% · 70th percentile · CISA · añadido el 2026-11-18
- CVE-2026-40217: BerriAI LiteLLMBerriAI LiteLLM Unprotected Alternate Channel Vulnerability · EPSS 17% · 97th percentile · CISA · añadido el 2026-11-18
- CVE-2026-90817: Vanderbilt University Research Electronic Data Capture (REDCap)Vanderbilt University Research Electronic Data Capture (REDCap) Code Injection Vulnerability · EPSS 3.7% · 90th percentile · CISA · añadido el 2026-11-18
- CVE-2026-90436: Apache AxisApache Axis Unsafe Reflection Vulnerability · EPSS 1.1% · 67th percentile · CISA · añadido el 2026-11-18
- CVE-2026-115731: Perforce Puppet EnterprisePerforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability · EPSS 0.7% · 53rd percentile · CISA · añadido el 2026-11-17
- CVE-2026-114713: UnrealIRCd UnrealIRCdUnrealIRCd Improper Neutralization of Delimiters Vulnerability · EPSS 0.5% · 41st percentile · CISA · añadido el 2026-11-13
- CVE-2026-123039: Check Point Multiple ProductsCheck Point Multiple Products Incorrect Permission Assignment for Critical Resource Vulnerability · EPSS 1.9% · 80th percentile · CISA · añadido el 2026-11-13
- CVE-2026-124194: Microsoft OfficeMicrosoft Office Outlook Missing User Interaction for Potentially Unsafe Action Vulnerability · EPSS 1.6% · 76th percentile · CISA · añadido el 2026-11-10
Government cyber advisories
From CISA, the UK NCSC, CERT-EU and Canada's Cyber Centre.
- SmarterTools security advisory (AV26-1177)Canadian Centre for Cyber Security ·
- JetBrains security advisory (AV26-1176)Canadian Centre for Cyber Security ·
- Cisco security advisory (AV26-1175)Canadian Centre for Cyber Security ·
- F5 security advisory (AV26-1174)Canadian Centre for Cyber Security ·
- GNU security advisory (AV26-1173)Canadian Centre for Cyber Security ·
- GitHub security advisory (AV26-1172)Canadian Centre for Cyber Security ·
- Google security advisory (AV26-1171)Canadian Centre for Cyber Security ·
- Oracle Corporation security advisory (AV26-1170)Canadian Centre for Cyber Security ·
New critical vulnerabilities
27 rated critical (CVSS 9.0+) in the last 3 days by the U.S. National Vulnerability Database.
- CVE-2026-114881 · CVSS 9.1 · EPSS 0.5% · 44th percentileVulnerability in the Document Management and Collaboration product of Oracle E-Business Suite (component: Attachments). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attack ·
- CVE-2026-91469 · CVSS 9.4 · EPSS 0.4% · 38th percentileVulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected are 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 and 15.1.1.0.0. Easily exploitable vulnerability allows unauthe ·
- CVE-2026-115139 · CVSS 9.3 · EPSS 0.4% · 33rd percentileVulnerability in the Oracle Hyperion Infrastructure Technology product of Oracle Hyperion (component: Installation and Configuration). The supported version that is affected is 11.2.26.0.000. Easily exploitable vulnerability allows unauth ·
- CVE-2026-114956 · CVSS 9.3 · EPSS 0.4% · 33rd percentileVulnerability in the Oracle Hyperion Planning product of Oracle Hyperion (component: Security). The supported version that is affected is 11.2.26.0.000. Easily exploitable vulnerability allows unauthenticated attacker with network access ·
- CVE-2026-114934 · CVSS 9.3 · EPSS 0.4% · 29th percentileVulnerability in the PeopleSoft Enterprise PeopleTools product of Oracle PeopleSoft (component: Integration Broker). Supported versions that are affected are 8.61-8.63. Easily exploitable vulnerability allows unauthenticated attacker with ·
- CVE-2026-101691 · CVSS 9.3 · EPSS 0.4% · 29th percentileVulnerability in the Oracle Mobile Field Service product of Oracle E-Business Suite (component: Admin UI). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attacker with netwo ·
- CVE-2026-91507 · CVSS 9.3 · EPSS 0.3% · 27th percentileVulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.1.0. Easily exploitable vulnerability allows unauthenticated ·
- CVE-2026-130778 · CVSS 10Incus before 7.6.0 contains an authentication bypass vulnerability that allows remote attackers to authenticate as any trusted certificate by appending its public certificate to their presented TLS client chain. Attackers can append the ser ·
Ransomware claims, last 7 days
150 claims posted by ransomware groups in 7 days, 25 in the last 24 hours. These are the criminals' own claims, not verified; Spike counts them and names no victim. Data: ransomware.live.
By country
 Canadá
 Alemania
 India
 Emiratos Árabes Unidos
 México
 Australia
 Reino Unido
 Vietnam
By sector
Most active groups
thegentlemen 18qilin 15N0n 14PixelLeaks 13Vortex 7Curious Worm 6rhysida 6Booba Project 6lockbit5 5akira 5
Cyber redacciones, every 5 minutes
7 of 8 security redacciones answered in the last check.
- US enlists private firms to cut scammers off from victims’ cashHelp Net Security ·
- Africa Retakes Top Spot as Most Attacked Region, Led by Nigeria SurgeDark Reading ·
- PHP Readies Critical Security Updates to Patch Another RCE FlawSecurityWeek ·
- Game consoles and Teslas are slipping past OT network segmentationHelp Net Security ·
- AI agents inherit employee access, and nobody’s watching how they use itHelp Net Security ·
- PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19The Hacker News ·
- Palo Alto Networks to Buy AI Startup Applied Compute for $4.5 BillionSecurityWeek ·
- Quantum position verification could lock remote hackers out, NIST showsHelp Net Security ·
- Ransomware access brokers are moving their deals off public forumsHelp Net Security ·
- Azure Linux 4 puts the OS behind Microsoft’s cloud services on your VMs at no extra license feeHelp Net Security ·
- Russia's Cold Relic APT Turns One Cloud Breach Into AnotherDark Reading ·
- Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilitiesCyberScoop ·
Companies disclosing cyber incidents
U.S. public companies must file Form 8-K Item 1.05 with the SEC within four business days of deciding a cyber incident is material. Filings from the last 120 days, from SEC EDGAR.
- Park Dental Partners, Inc. (PARK)Form 8-K, Item 1.05 · filed 2026-10-13 · all filings
- Astrana Health, Inc. (ASTH)Form 8-K, Item 1.05 · filed 2026-09-23 · all filings
- BOSTON SCIENTIFIC CORP (BSX)Form 8-K, Item 1.05 · filed 2026-09-08 · all filings
- Park Dental Partners, Inc. (PARK)Form 8-K, Item 1.05 · filed 2026-09-01 · all filings
- Nutex Health Inc. (NUTX)Form 8-K, Item 1.05 · filed 2026-08-31 · all filings
- AMGEN INC (AMGN)Form 8-K, Item 1.05 · filed 2026-07-31 · all filings
- River Financial Corp (RVRF)Form 8-K, Item 1.05 · filed 2026-07-30 · all filings
Internet outages by country, last 24 hours
Disruptions detected by IODA at Georgia Tech from routing, active probing and traffic data. A disruption can be a cut cable, a power failure, an attack or a government shutdown; IODA reports the drop, not its cause.
 Belice Criticalrouting (BGP), Google traffic · · country risk
 Guatemala CriticalGoogle traffic · · country risk
 Colombia CriticalGoogle traffic · · country risk
 Costa Rica CriticalGoogle traffic · · country risk
 Ecuador CriticalGoogle traffic · · country risk
 Nicaragua CriticalGoogle traffic · · country risk
 Honduras CriticalGoogle traffic · · country risk
 Turkmenistán Criticalactive probing, routing (BGP) · · country risk
 RD del Congo Criticalrouting (BGP), Google traffic · · country risk
 Haití CriticalGoogle traffic, routing (BGP) · · country risk
Threat actors in the news, 7 days
Groups named in security newsroom headlines and government advisories. Linked to their MITRE ATT&CK profile where one exists.
Malware seen in the last 24 hours
888 indicators of compromise shared on abuse.ch ThreatFox.
Unknown malware 145Mirai 138IClickFix 62Vidar 47Raven Stealer 45ClearFake 29XWorm 25Unknown Loader 24Formbook 21Sliver 20php.shin_webshell 18Agent Tesla 18
Spike Pro can watch the vendors and products your organization runs (for example Fortinet, Citrix, Microsoft Exchange) and notify your team the moment CISA confirms exploitation, a critical vulnerability is published, or a government advisory names them. Spike Pro →
Lo que el mundo busca — Ciberseguridad
Alerta conflicto, interrupción o escándalo · Sube rápido sube rápido · En aumento growing · Pulso 0–100: 90+ Explotando · 70+ Al rojo vivo · 40+ Calentándose
Java


 · hace 26 h
Nginx

 · hace 13 h